In many networks, every administrator signs in directly on the switch with a local account. Afterwards it is hard to say who was where and when. TACACS+ is a protocol for central logins to network devices. At sign-in, the switch asks a TACACS+ server and sends it accounting data.
The service is included
AIM comes with its own TACACS+ service. It runs next to the application as a separate service with its own database. You do not need a third-party TACACS+ server. In the network module, TACACS+ is the interface to this service.
What you maintain in AIM
- Users who may sign in to network devices
- Clients, meaning the network devices that query the service
- Access rules (Access Control)
- Accounting with the latest sessions
The dashboard shows users, clients and the latest sessions on the switches. It covers the devices that send their accounting to the TACACS+ server.
Traceable in AIM
The service itself keeps no change history. Since version 3.7.8, AIM records what it sends to TACACS+, with the values before and after. Changes made directly on the service, bypassing AIM, are not recorded there.
Part of the network module
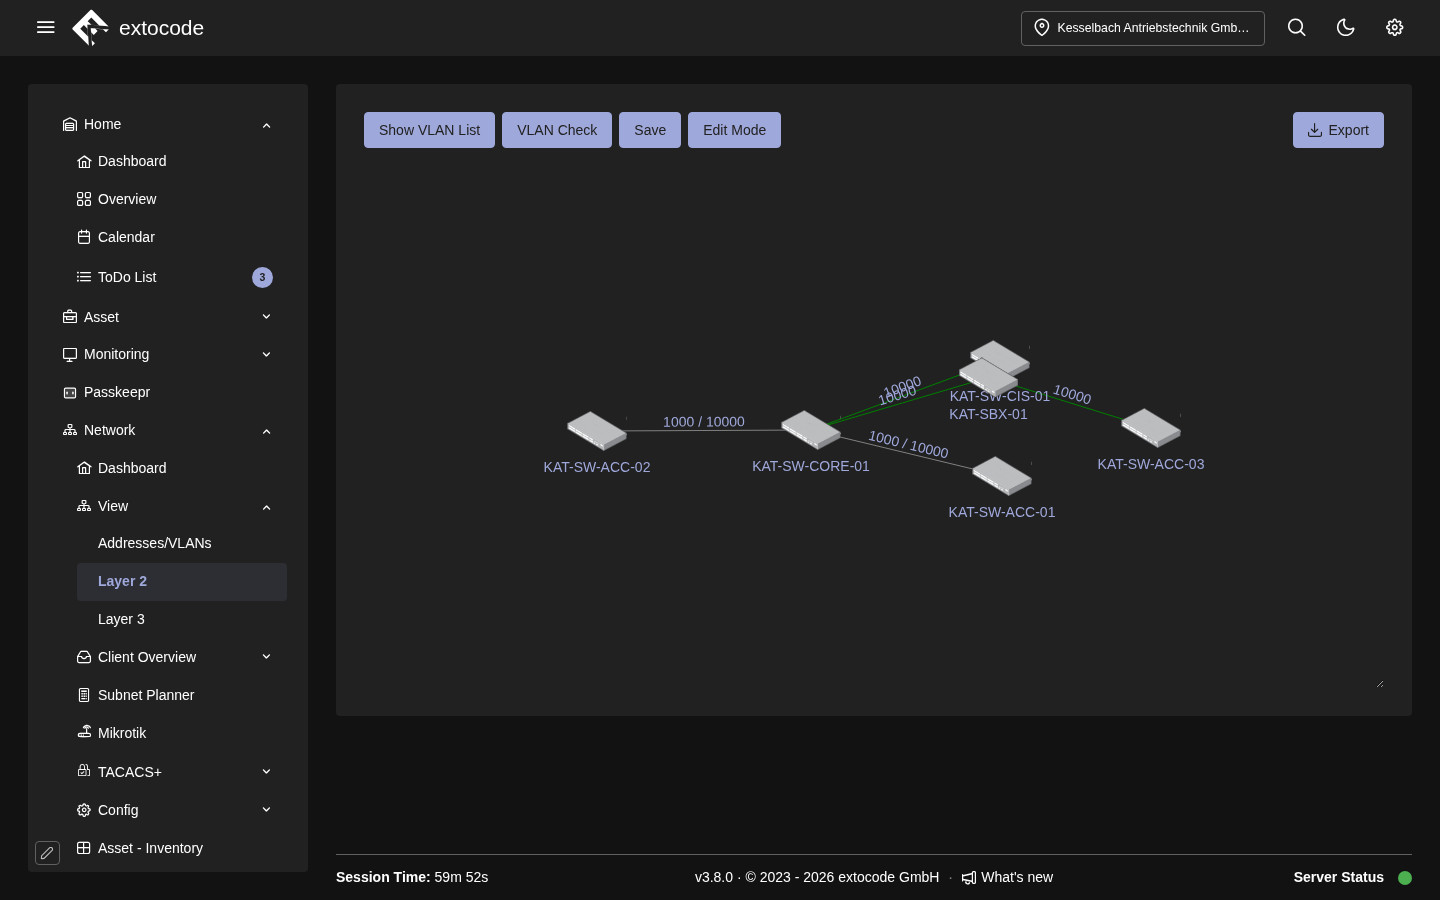
The network module reads ports, VLANs and clients from network devices of nine vendors. For Cisco, Ruijie and Allied Telesis, AIM switches ports and tests cables. The TACACS+ module does not connect MikroTik devices. TACACS+ is included in the seat and tenant price. More on the modules page.
In the COD demo, the accounts Demo First Level and Demo Second Level see the TACACS+ dashboard. The login details are on extocode.com/demo.
The AIM interface is in English. Which functions your contract covers is set out solely in the service description in the version that applies to your contract.