Where does a company stand on ISO 27001 or NIS2? The answer is usually spread across risk analysis, policies, supplier contracts and the knowledge of individual people. The AIM GRC module brings this together in one platform. It has grown considerably since version 3.7.
Standards and catalogues
Included are ISO/IEC 27001:2022, ISO/IEC 27002:2022, ISO 9001:2015, ISO 22301:2019 and the NIS2 Directive. You can switch on ISO/IEC 27019, the BSI IT-Grundschutz Compendium 2023 and the BSI guidance on the use of attack detection systems. An administrator uploads the texts of the BSI catalogues.
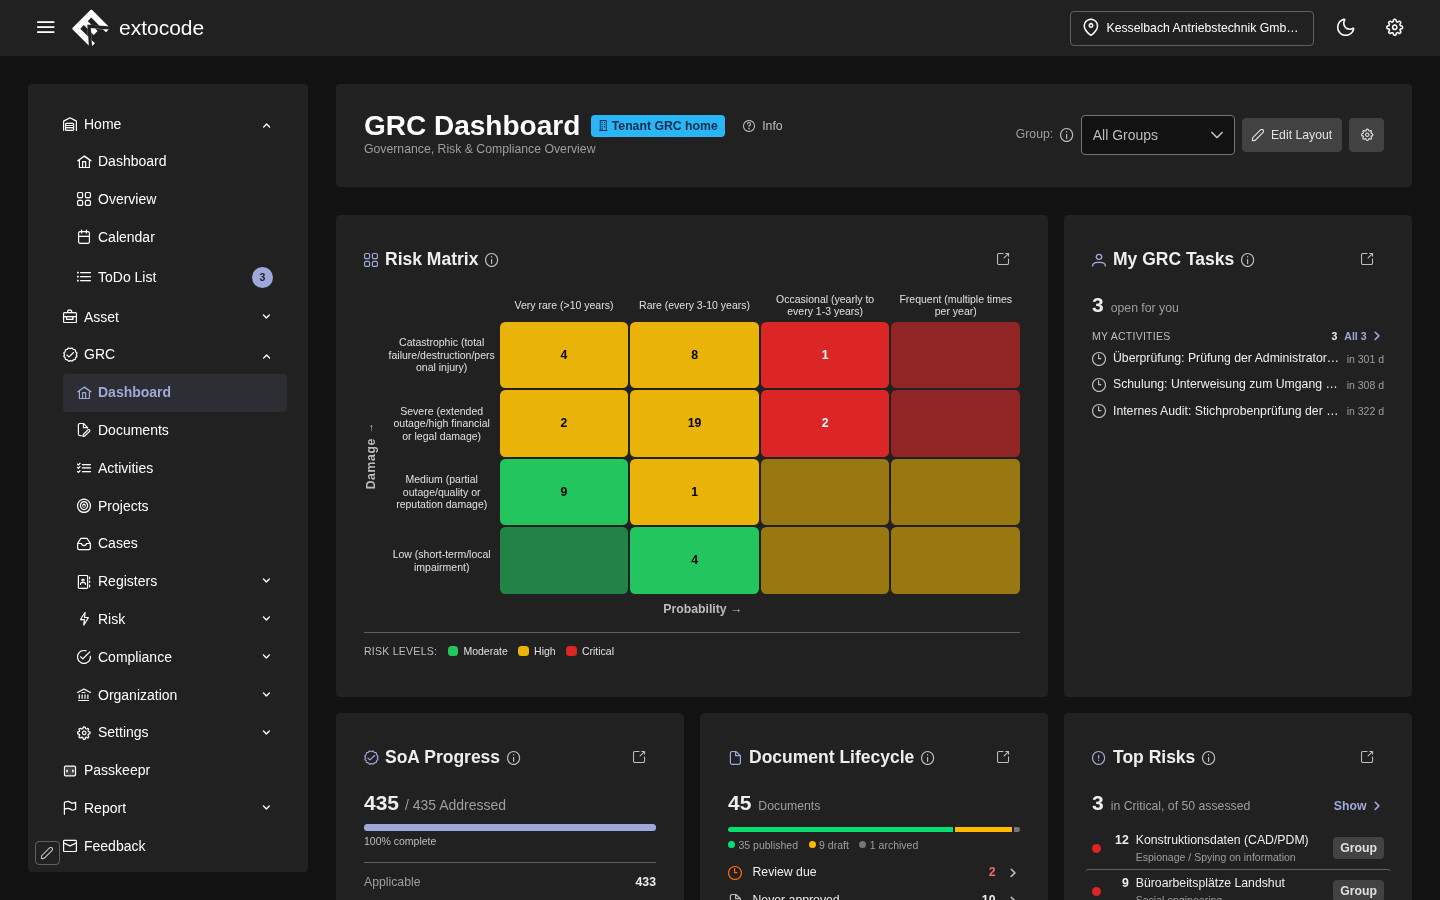
The Statement of Applicability (SoA) states for each requirement whether it applies, how far it is implemented and which document proves it. The requirement texts can be shown in German, also in the SoA as a PDF. They are paraphrased and not the wording of the standards.
Registers and suppliers
Since version 3.7.3 there are registers for processes and suppliers. For each supplier you see which evidence it owes, such as a questionnaire, an audit or a certificate, and its current status. Links between assets, processes and suppliers pass on the protection level. The risk analysis follows BSI Standard 200-3.
Forms, approvals and deadlines
- Forms with signatures and a PDF at completion.
- Approvals with four eyes, as a switch per tenant, enabled by default.
- KPIs per period, training and activities with deadlines and repetition.
- An incident involving personal data creates a case with a 72 hour review deadline under the GDPR. AIM does not report anything to an authority.
One audit log for the whole platform
Since version 3.7.8 the audit page shows changes, sign-ins and exports from the whole platform. Every night AIM seals the new rows in a signed checkpoint. A row that was changed, deleted or inserted later becomes visible this way.
What GRC does for NIS2
The GRC module helps you prepare for NIS2. It maps the requirements, links them with risks, documents and suppliers and helps you document where you stand. AIM does not replace legal advice. Whether your measures are sufficient is assessed by you and your advisers.
More on the compliance page. In the COD demo, the account Demo GRC shows the risk matrix, the SoA and suppliers with the data of a fictitious industrial company.
The AIM interface is in English. Which functions your contract covers is set out solely in the service description in the version that applies to your contract.